Connect users to applications, not the entire network
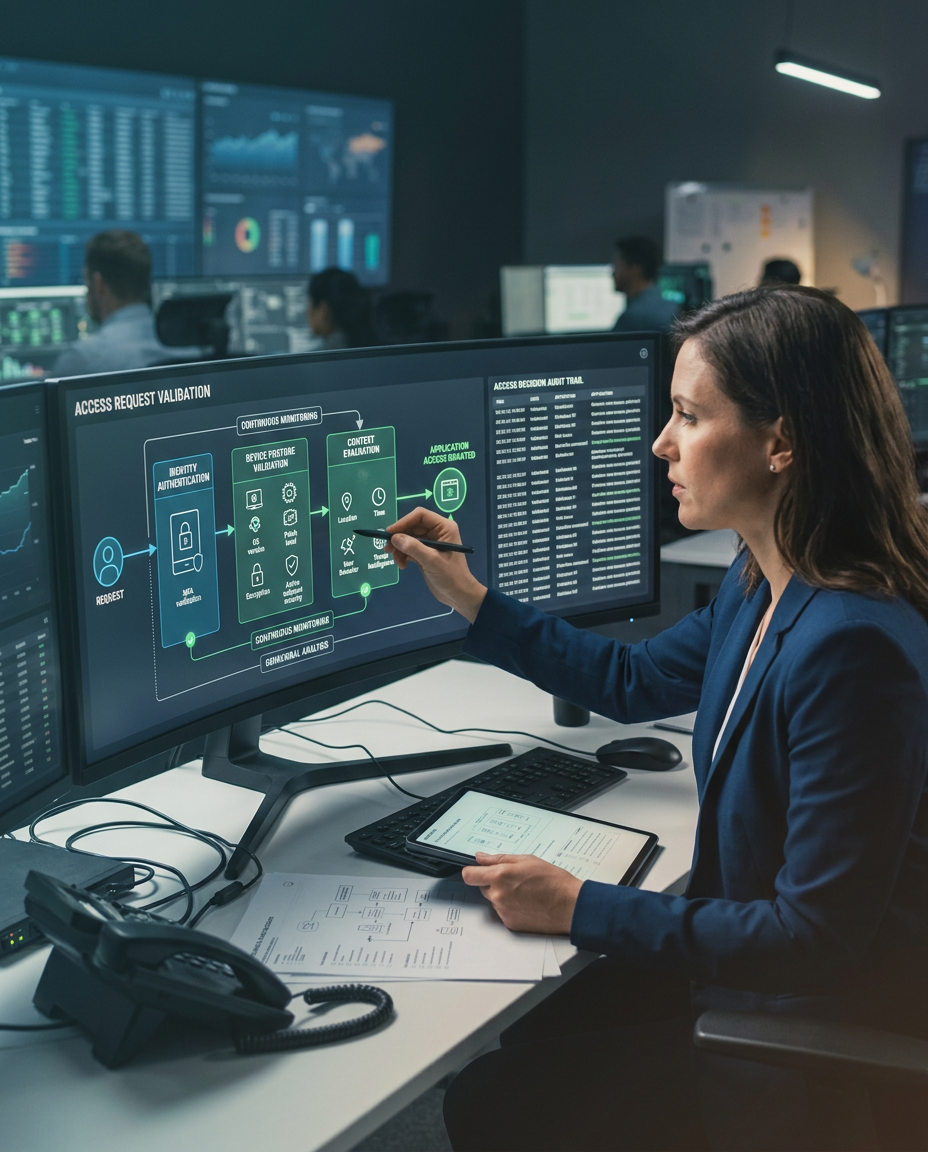
Reduce implicit trust and grant access only to the applications each user needs, under the right conditions.
Granting access should no longer mean extending the network to the user. In hybrid environments, with applications distributed across data centres, cloud and SaaS, this model can unnecessarily expand the accessible attack surface once an identity has been authenticated.
At Evolutio, we implement ZTNA to establish direct, controlled connections between authorised users and authorised applications, assessing identity, device and context before granting access and enforcing least privilege.
We integrate this capability with identity, MFA, device posture, segmentation and observability so that access decisions can adapt to risk without adding unnecessary complexity for users.
Redefining the scope of trust
From VPNs and network trust to application-based access
Traditional remote access models typically place users within a network segment once they have authenticated. Extending trust in this way creates more opportunities for lateral movement and requires organisations to protect an increasingly blurred perimeter.
ZTNA changes the basis of the decision: it asks not just who is connecting, but which specific application they should access, from which device and under what conditions. At Evolutio, we connect this policy with identity, device posture, segmentation and observability to adapt access to risk.
Context before access
The elements of a Zero Trust decision
ZTNA works when decisions combine sufficient signals and access is restricted to the required resource. The aim is to reduce exposure without making every access request a complex experience for users.
Identity, device and context determine whether a request meets the defined conditions. Application-based access then limits the scope of that trust to the authorised resource, without providing broad visibility into the private network.
Identity
We validate the user, group, role and authentication by integrating with the identity provider and MFA.
Device
We consider management status, security posture, operating system and other trust signals where available.
Context and risk
We incorporate location, application, sensitivity and risk signals to adapt policies.
Application-based access
We connect users to the authorised resource without granting broad visibility into the private network.
A phased transition for remote access
Migrate access without disrupting users
ZTNA often coexists temporarily with VPNs and other access mechanisms. The transition must map out applications, user profiles and dependencies to prevent security changes from degrading the user experience.
We therefore prioritise access use cases, integrate the necessary signals and validate policies with controlled groups before expanding coverage. Telemetry gathered during the transition helps refine decisions and progressively retire legacy access paths when they are no longer needed.
Prioritise
We classify applications, user groups, third parties and access scenarios.
Integrate
We connect identity, MFA, device posture and application connectors.
Pilot
We validate policies and user experience with controlled groups and representative use cases.
Scale
We expand coverage, reduce legacy access and refine policies using real-world telemetry.
An access decision informed by multiple capabilities
Zero Trust is a policy, not a standalone product
ZTNA becomes more effective when coordinated with identity, endpoint, network and detection capabilities. Exceptions, third parties, privileged accounts and legacy applications need explicit handling to prevent the migration from recreating parallel paths of trust.
At Evolutio, we connect these capabilities so that access decisions remain consistent throughout their lifecycle: from initial authentication to changes in context and signals that may warrant subsequent review, restriction or revocation.
Least privilege. We grant only the access required to the authorised resource within the approved context.
Third-party access. We keep suppliers and external collaborators separate from the internal network and limit their access scope.
User experience. We measure availability and performance to ensure controls do not create unnecessary friction.
Operations and response. We log access decisions and connect relevant signals with SOC and ITDR capabilities where applicable.
Bringing trust closer to the resource
Less network exposure, more context for every decision
At Evolutio, we use ZTNA to reduce implicit trust and bring access controls closer to the resource each user actually needs.
The aim is to replace broad network access with specific decisions based on identity, device, context and application, bringing security and user experience together within a single operating model.